
What is cybersecurity governance, risk, and compliance (GRC)?
If you have been digging into cybersecurity, and particularly if you are utilising the NIST cybersecurity framework to guide your company’s protocols, you have probably heard the acronym “GRC.” But what IS GRC, and what do its constituent parts mean for your company’s cybersecurity infrastructure?
According to CIO.com:
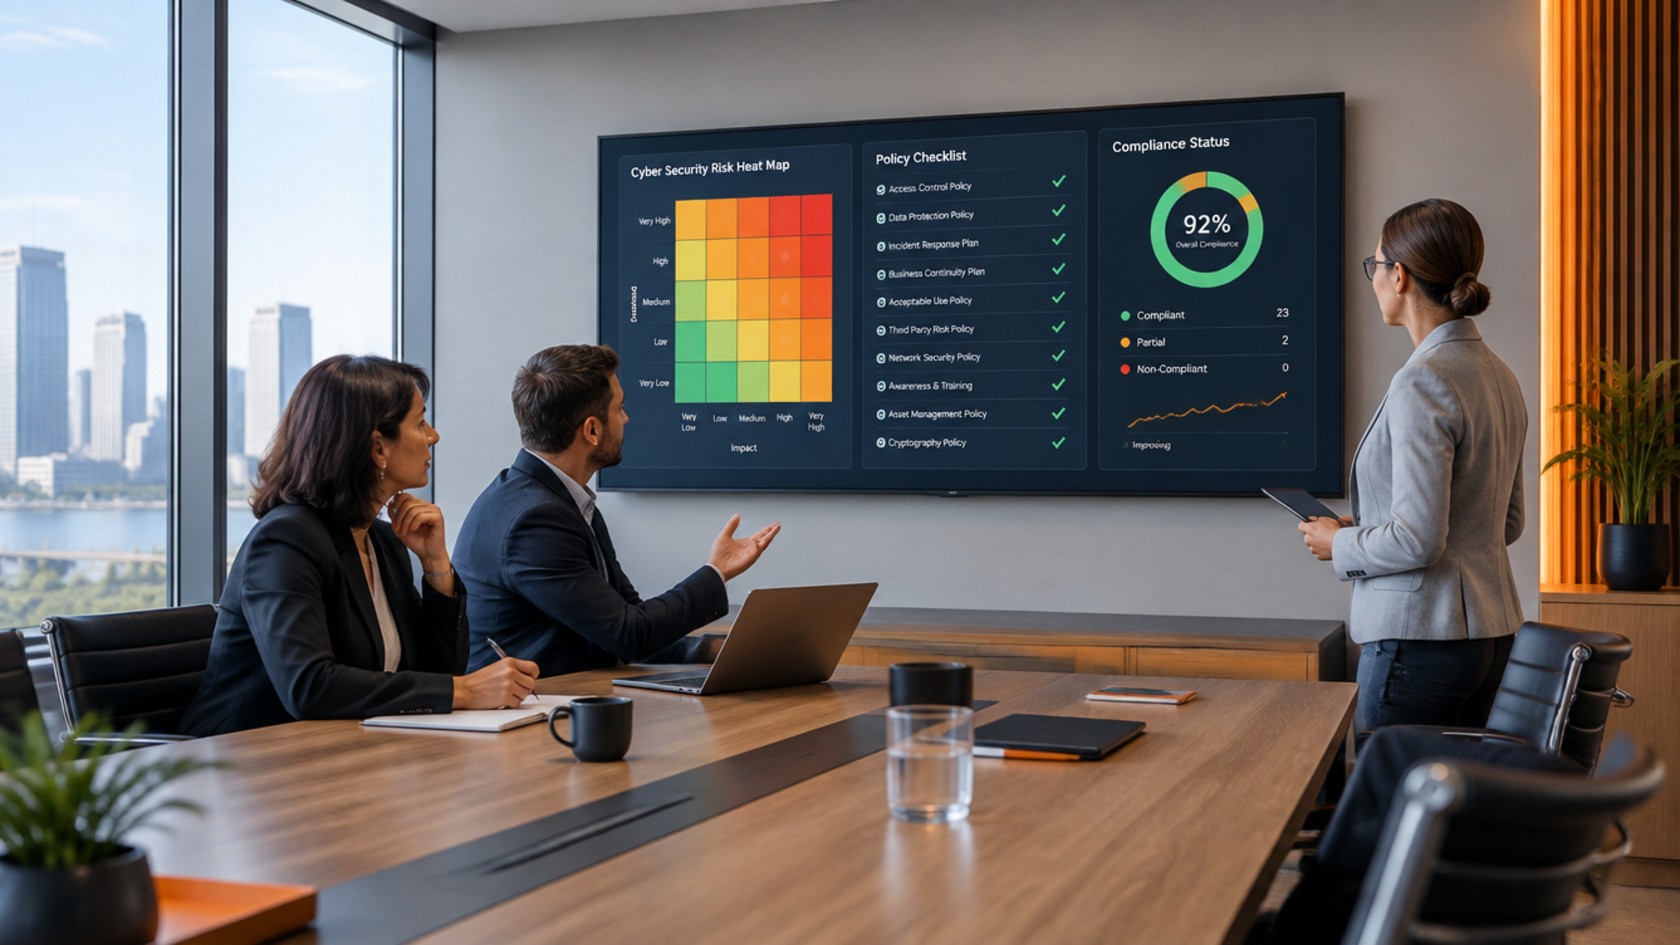
Governance, risk, and compliance (GRC) is an operational strategy for managing an organization’s overall governance, enterprise risk management, and regulation compliance efforts. This disciplined approach enables an organization to align its governance, risk, and compliance endeavors to its strategic goals, business objectives, and the technology that enables its operations.
Even though governance, risk, and compliance are interrelated, and cybersecurity GRC should be considered jointly in your framework, let’s discuss each component separately before circling back to GRC overall.
Governance
In this context, cybersecurity governance relates to the organisational plan for cybersecurity and information security. As the University System of Georgia explains:
Effective security governance is managed as an organizational-wide issue that is planned, managed and measured in all areas throughout the organization. In IT Governance, leaders are accountable for and are committed to providing adequate resources to information security.
They go on to list a number of principles that should guide thinking on cybersecurity governance. These include the suggestion that companies should:
- Conduct an annual cybersecurity evaluation, review the evaluation results with staff, and report on performance.
- Conduct periodic risk assessments of information assets as part of a risk management program.
- Implement policies and procedures based on risk assessments to secure information assets.
- Establish a security management structure to assign explicit individual roles, responsibilities, authority, and accountability.
Governance is now built into the NIST Cybersecurity Framework itself: CSF 2.0, released in February 2024, added a Govern function covering how an organisation’s cybersecurity risk management strategy, expectations and policy are established, communicated and monitored. In Australia, ASD and the Australian Institute of Company Directors (AICD) advise that boards should treat cyber security as a core governance and enterprise risk.
Once a system of governance has been established and clearly defined, the second component of cybersecurity GRC, an assessment of risk, can begin.
Risk
The next step in creating a GRC-driven cybersecurity infrastructure is to assess risk. You will want to understand your current cybersecurity infrastructure and any potential gaps in your system. As StickmanCyber explains, a comprehensive risk analysis will attempt to:
- Understand your specific business context and cybersecurity requirements
- Identify existing gaps and vulnerabilities in your security posture
- Share a comprehensive list of recommendations to mitigate vulnerabilities and close security gaps
Those recommendations should, ideally, be aligned with your company’s overall strategies, and also with any mandated (or desired) cybersecurity compliance frameworks.
Compliance
Certain industries require specific cybersecurity certifications in order to be compliant with governmental or industrial protocols. The third part of cybersecurity GRC involves developing a thorough understanding of those frameworks and ensuring that your organisation is in compliance. In Australia, for example, APRA-regulated entities must meet APRA CPS 234, and organisations covered by the Privacy Act 1988 must protect the personal information they hold and report eligible data breaches under the Notifiable Data Breaches scheme.
While there are a number of frameworks in place, including the NIST Cybersecurity Framework, ISO 27001 Certification, PCI DSS Compliance and ASD’s Essential Eight, most frameworks will involve a thorough consideration of your GRC.
Bringing governance, risk and compliance together
Governance, risk, and compliance play a vital role in any cybersecurity plan. Evaluating your needs and risks will help you to keep your business, and your clients’ information, safe.
Ready to Improve and Enhance Your Cybersecurity Posture? Know your exact challenge and want a solution partner? Just starting to evaluate your cybersecurity GRC requirements?
The StickmanCyber team can help.
The First Step is Crucial. Start with a Cybersecurity Assessment.
Frequently asked questions
Where does the term GRC come from?
The Open Compliance and Ethics Group (OCEG), a non-profit think tank, says it originated the GRC concept in 2002. OCEG describes GRC as the integrated collection of capabilities that enable an organisation to reliably achieve objectives, address uncertainty and act with integrity.
What is the difference between GRC and cyber security?
Cyber security is the set of controls and practices that protect systems and data, such as patching, access control and monitoring. GRC is the management layer around them: governance sets direction and accountability, risk management decides which threats matter most, and compliance checks that the organisation meets its legal, regulatory and contractual obligations. Together they help make sure security effort goes where the risk is.
Which GRC obligations apply to Australian organisations?
It depends on your sector and size. Organisations covered by the Privacy Act 1988 must take reasonable steps to secure personal information and notify eligible data breaches. APRA-regulated entities must meet CPS 234, responsible entities for certain critical infrastructure assets must maintain a risk management program under the SOCI Act, and businesses with an annual turnover of $3 million or more must report ransomware payments within 72 hours under the Cyber Security Act 2024.
Who is responsible for GRC in an organisation?
Ultimately, the board and senior executives. ASD and the AICD advise boards to treat cyber security as a core governance and enterprise risk, and APRA’s CPS 234 makes the Board of a regulated entity ultimately responsible for its information security. Day-to-day work is usually led by a chief information security officer, or a virtual CISO, working with risk, compliance and IT teams.
How often should a cyber risk assessment be done?
Regularly, rather than as a one-off project. ISO/IEC 27001, for example, requires information security risk assessments at planned intervals or when significant changes are proposed or occur, such as a new system, supplier or business process. The University System of Georgia principles above suggest an annual cybersecurity evaluation alongside periodic risk assessments.
Do Australian businesses have to follow the Essential Eight?
No law requires most private businesses to implement it. Under the Protective Security Policy Framework, non-corporate Commonwealth entities have been required since 1 July 2022 to implement all eight strategies to at least Maturity Level Two. ASD developed the Essential Eight to help organisations protect themselves against cyber threats, and any business can use its maturity model to assess and improve its security.