01

Build a Secure Network
Segment and defend the environment where card data lives.
- Network security controls
- Secure system configurations
- Protect stored account data
- Encrypt data in transit
Staying compliant is about more than ticking boxes. Our PCI DSS experts help you protect cardholder data, reduce risk and meet compliance requirements through a streamlined, business-friendly approach.
Understand your gaps. Define your roadmap · Get certified faster
 Join 200+ organisations already protected across ANZ


US$33bn - Annual global card fraud losses across the payments industry

Version 4.0.1 raised the bar: stronger authentication, continuous rather than annual thinking, and evidence for every control.

82% of website code and actions are outside an organisation's direct control, increasing payment security risk
PCI DSS validation is annual, but the obligation is continuous. A gap between attestations is where the real exposure sits.

Segment and defend the environment where card data lives.
Keep malicious code out, and keep access to card data on a need-to-know basis.
Prove the controls keep working — not just that they existed on audit day.

Build trust with customers

Reduce overall data breaches

Improve brand reputation

Assessment of the current environment wrt PCI DSS standards

Plan of remediation to achieve the required standard.

Manage remediation actions required to achieve compliance

Review of all remediation activities and certification of compliance

On-going maintenance and proactive support
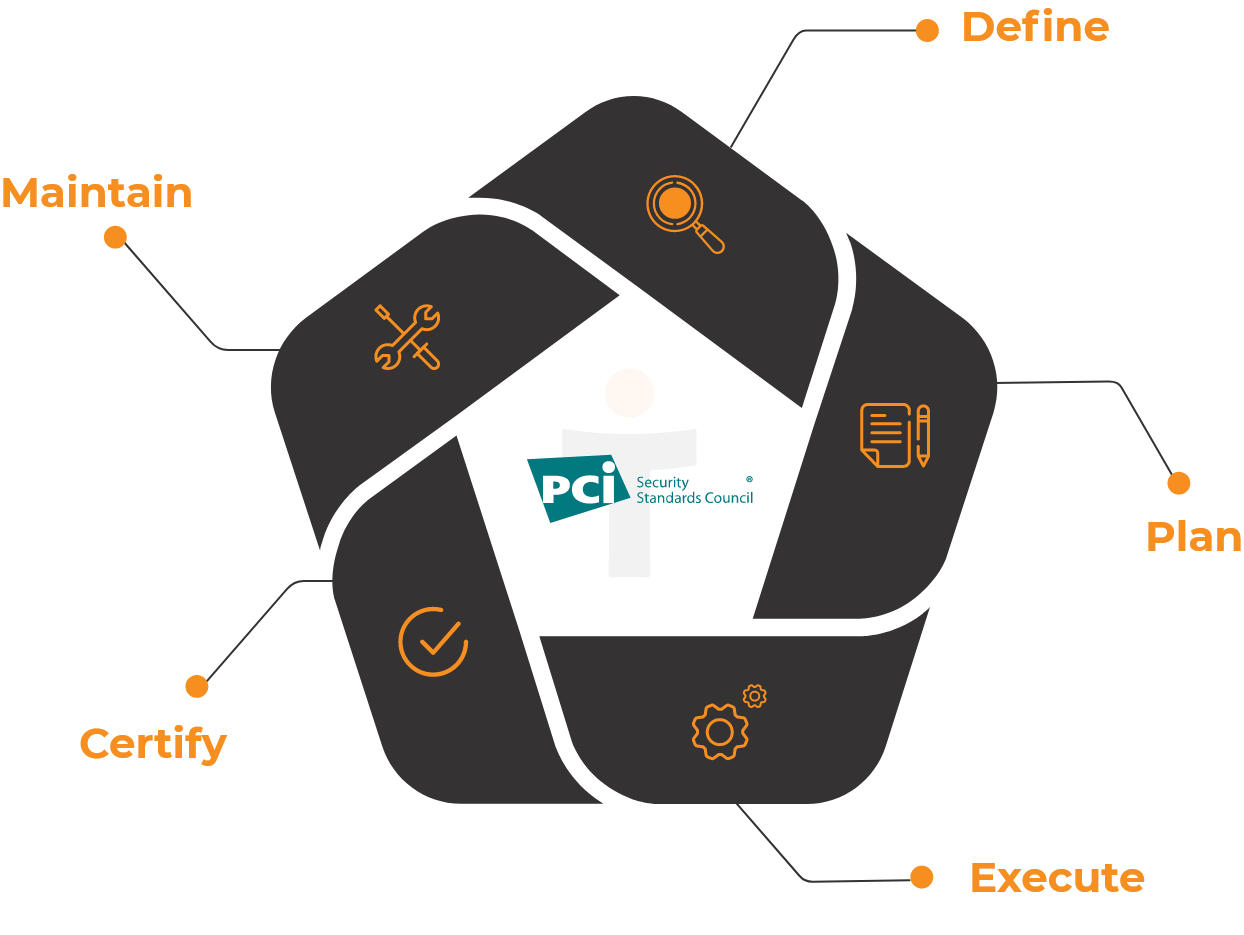
We deliver Cybersecurity-as-a-Service, simplifying PCI DSS from scope to attestation. Your team stays focused on payments while we run the assessment, remediation and validation process.


How a leading property company consolidated cybersecurity vendors, reduced costs by 40%, and achieved complete compliance in under 6 months.
StickmanCyber provided a turn-key solution for us to develop, achieve and maintain ISO27001 security certification, including 24x7x365 days security operations with monitoring, detection, and response.
We found their team to be extremely proficient and knowledgeable and the project was completed ahead of schedule.

During all our engagements, StickmanCyber have proved themselves to be genuine and honest, ramping resources up and down (as required), and adding expertise such as project managers, to ensure overall success.
I would be happy to recommend them to any organisation large or small to help with cybersecurity challenges.

After multiple attempts to find suitable, trustworthy, consistent, and reliable cybersecurity partners, we engaged with StickmanCyber, who are a QSA for PCI DSS and CREST ANZ Registered entity for Penetration Testing.
StickmanCyber has worked with us in guiding and assisting us to understand our requirements for cyber security.

Achieving ISO 27001 certification was a critical milestone for us. StickmanCyber's team demonstrated an in-depth understanding of our business.
Their comprehensive support included everything from conducting risk assessments and identifying vulnerabilities to implementing robust security protocols and preparing us for the rigorous ISO audit process.

Partnering with StickmanCyber for our ISO27001 certification was a game-changer for us. From the very beginning, their team made a complex and often overwhelming process feel straightforward and achievable.
They took the time to really understand our business needs, tailoring their approach to fit our specific challenges. We were always one step ahead.

Knowing that we’d be guided through the process and that StickmanCyber would handle policy creation and project management allowed us to focus on our core business.
Whether it’s ISO certification, internal audits, or ongoing compliance management, StickmanCyber provides the tools, guidance, and support to help organizations succeed.


