
In today’s world, no business is safe from cybercrime, there has been a steady wave of cyber attacks in the news, but a much larger number goes unreported. In Australia alone, ASD’s Australian Cyber Security Centre received over 82,000 cybercrime reports in 2025–26, on average one every six minutes. The need for cybersecurity has only heightened in the past few years. Regardless of business type, size or nature, a cybersecurity strategy needs to be implemented to fight back against malicious actors looking to compromise information security.
This is easier said than done. Implementing a comprehensive cybersecurity program can take a lot of effort and resources. However daunting these costs may seem, they are severely outweighed by the legal, financial, and reputational repercussions an organisation faces if a security incident were to occur. Many organisations, especially small to medium enterprises have looked to outsource their cybersecurity needs to managed service providers or cybersecurity specialists, rather than have an in-house solution.
Both in-house and outsourced solutions can develop a comprehensive cyber security plan for your business, so which do you choose? Below we outline at a high level, what the benefits are for each solution.
The Business Case For In-House Cybersecurity
Better control
Having an in-house cybersecurity team allows you to have better control over who has access to your systems and networks. An increase in visibility when it comes to the activity of your internal information security team ensures that resources are being used efficiently and effectively. In-house security teams can also be privy to all business initiatives, goals, and objectives, which can result in a higher chance that security goals are aligned with business goals. Building an overarching culture of cyber security can be a challenge when working with an outsourced cybersecurity provider, on the other hand, this is much easier to do when your cybersecurity solutions are in-house.
Deeper knowledge of the business
An in-house cybersecurity team also has a deeper understanding of the business’s systems and networks but also know who’s who in the business, they know about the day-to-day operations and the ongoing projects. What this means is that when implementing technical changes they have an easier time understanding its impact on the business and how to best minimise downtime in the event of a security incident due to their better understanding of the critical areas of the business. In-house teams also can be more responsive than outsourced service providers, given that their only priority is your business.
Merges well with your existing physical security team
With the increase in importance given to cybersecurity as businesses adapt to our new digital environment physical security can sometimes be overlooked. However physical along with cybersecurity needs to be prioritised equally, the strongest cybersecurity measures such as antivirus software, will not protect against a malicious actor stealing storage devices from your office environment. Given the increase in technology when it comes to physical security, IT and physical security teams in organisations should work together as cross-functional teams rather than existing as separate functions within an organisation. This is easier to achieve when working with an in-house cybersecurity solution versus an outsourced cybersecurity solution.
The Business Case For Outsourcing Cybersecurity
Wide range of skills and expertise
The threat landscape is constantly evolving, with criminals only getting more sophisticated and ingenious in their methods of attack. Due to this cybersecurity specialists have had to up their game to match these criminals. To effectively manage information security risks, organisations require the help of dedicated professionals with extensive experience in a wide number of industries. These dedicated professionals should have deep knowledge and understanding of the tactics, techniques, and procedures of cybercriminals. It is unrealistic for many organisations to host a cybersecurity team in-house that consists of these kinds of professionals. Therefore by outsourcing their cybersecurity, organisations can gain access to specialists who have extensive industry experience, knowledge, and skills.
A more affordable option
Cybersecurity is no longer a luxury for organisations, it has quickly become a necessity that needs to be adhered to daily. According to IBM’s Cost of a Data Breach Report 2026, the global average cost of a data breach was USD 4.99 million, based on breaches at 602 organisations between March 2025 and February 2026. In Australia, the average self-reported cost of cybercrime per business report to ASD rose 16% to $93,500 in 2025–26. Hiring a team of specialists who are skilled in different facets of cybersecurity can help reduce the risk of a data breach occurring within your organisation. However, hiring, training, and maintaining a cybersecurity team in-house can cost a huge margin. This cost can be brought down significantly if an organisation were to outsource its cybersecurity by hiring an external agency that is proficient in providing a wide range of protective services at customised costs.
Allows for a faster cybersecurity solution
Recruiting, training and retaining cyber security experts to research and set up security software and hardware can take many months. This means that many businesses could be waiting a long time for in-house cyber security protection that’s operating effectively. Instead, by outsourcing your cybersecurity needs to an experienced provider you have the peace of mind to focus on growing your business while a large team of skilled cybersecurity experts helps safeguard your sensitive information.
In-house or Outsourced?
Now that you have an idea of the advantages of both cybersecurity solutions, which one is right for your business? We believe that for many businesses a hybrid approach is what works best, a smaller in-house team along with the expertise of an experienced external provider can lead to a robust approach to cybersecurity.
For all businesses, especially small to medium businesses, cybersecurity can be a daunting investment and finding the right skill and experience can be a challenge, especially when your business operates in a niche market.
A niche market comes with its own unique set of cybersecurity challenges as the threat environment can be intricate and requires a high level of experience to deal with. By outsourcing your needs to a cybersecurity service provider, your niche business can get the attention it deserves, with access to a wide range of specialists, something that is unrealistic if cybersecurity was dealt with in-house. An outsourced cybersecurity solution can also be scaled up and down depending on how quickly your in-house cybersecurity capability is growing.
Cyber attacks can be extremely stressful, dealing with cyber threats is no mean feat, especially if your organisation dedicates the handling of its entire cybersecurity function to a small team. This small team will have to deal with security practices like continuous vulnerability management and around-the-clock monitoring to stay on top of their organisation’s information security, which can lead to employees being overwhelmed and overworked. Having the ability to rely on and lean on the skill and expertise of an outsourced cybersecurity solution reduces the stress and effort on your in-house cybersecurity team.
How can we help?
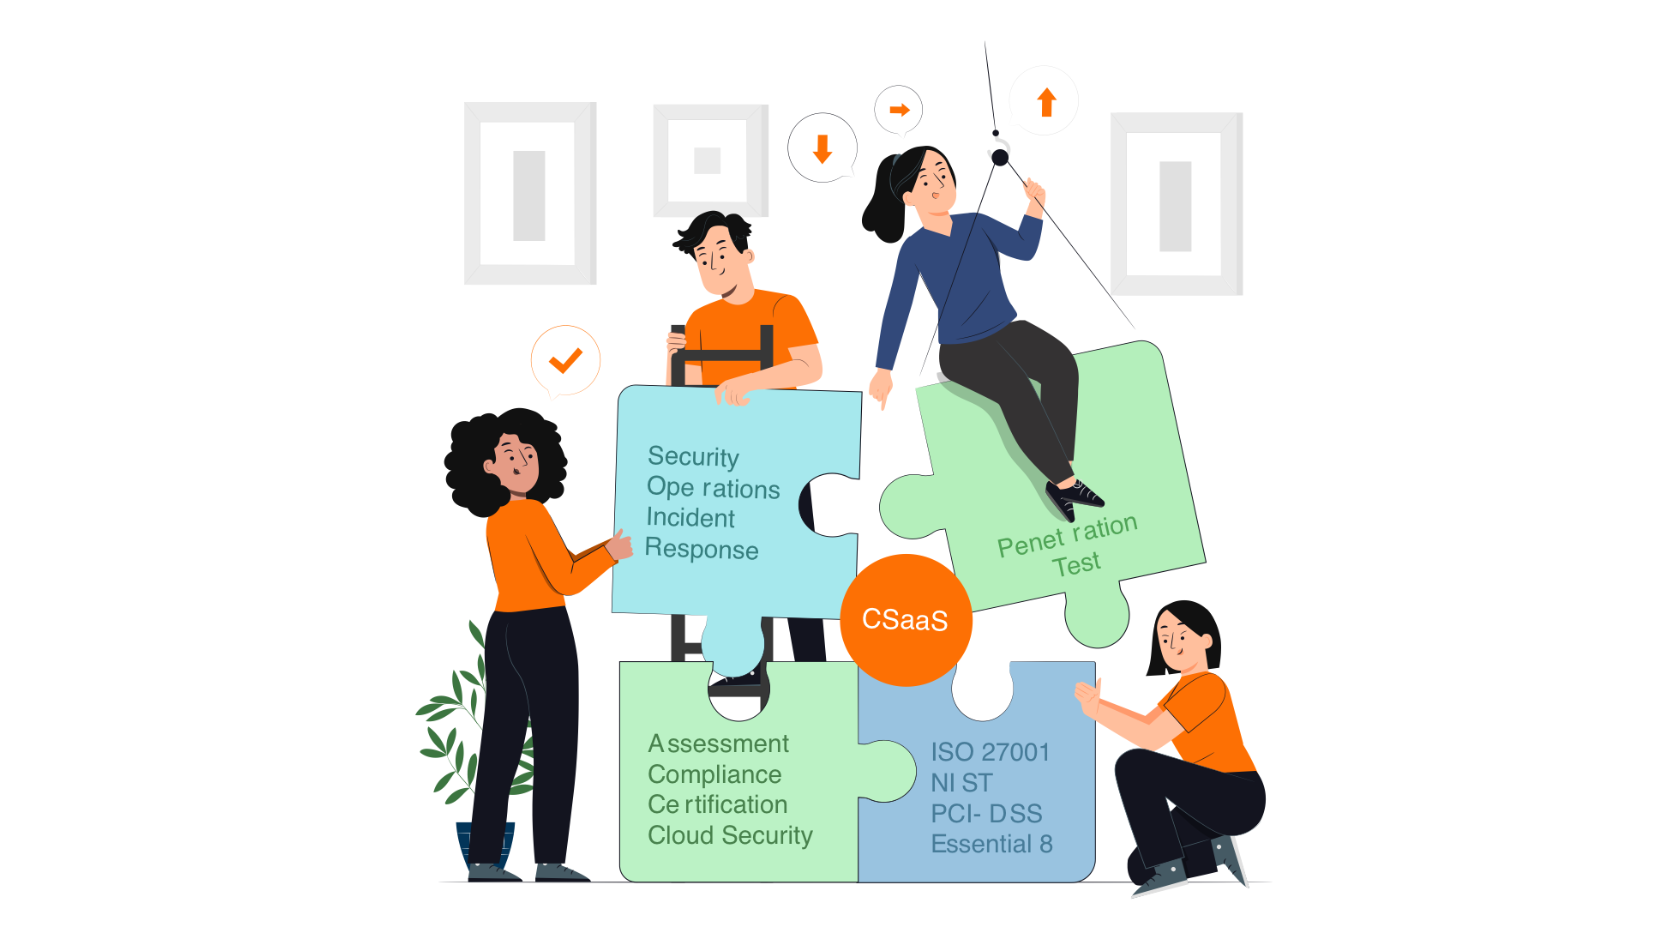
Now that you have a high-level understanding of the benefits of outsourcing, you might be curious to learn more about it. Get in touch with us today and get a free consultation with one of our experts to learn more about why you should be choosing to outsource your cybersecurity needs. Our Cybersecurity & Compliance Services offering provides businesses with an end-to-end cybersecurity solution at an affordable cost.
Frequently asked questions
What is outsourced cybersecurity?
Outsourced cybersecurity means engaging an external provider, such as a managed security service provider (MSSP), to deliver some or all of your security functions instead of employing a full in-house team. Common examples include 24/7 monitoring and incident response, vulnerability management, penetration testing and virtual CISO advice. You can outsource a single service or most of your security program.
Can you outsource accountability for cyber security?
No. You can outsource the work, but your organisation remains accountable for protecting its systems and data. For example, APRA’s Prudential Standard CPS 234 makes the Board of an APRA-regulated entity ultimately responsible for information security, and where a third party manages information assets, the entity must assess that party’s information security capability. Keep oversight of any provider through clear contracts, reporting and regular reviews.
What should you ask a managed security service provider before signing up?
ASD’s Australian Cyber Security Centre suggests asking managed service providers whether they implement better practice cyber security (such as the Essential Eight), securely administer their systems and services, monitor activity on those systems, regularly assess them, and are prepared for and able to respond to cyber security incidents. Its guidance, Questions to ask managed service providers, explains each question.
Is outsourcing cybersecurity a good option for small businesses?
Often, yes. Small and medium businesses rarely have the budget for a full team of security specialists, so outsourcing gives them access to a range of skills, such as monitoring, testing and advice, at a cost that suits their size. Start with your highest risks, keep someone internal responsible for security decisions, and scale the services as the business grows.
What is a hybrid or co-managed cybersecurity model?
In a hybrid (co-managed) model, a small in-house team keeps ownership of security strategy, business context and day-to-day decisions, while an external provider supplies specialist skills and capacity, such as 24/7 monitoring, penetration testing or incident response. It combines the business knowledge of an internal team with the breadth of a specialist provider, which is why we believe it suits many businesses.
What is a virtual CISO (vCISO)?
A virtual CISO is an outsourced security leader who provides chief information security officer expertise on a part-time or as-needed basis. A vCISO can set security strategy, report to the board and guide compliance without the cost of a full-time executive, which suits organisations that need security leadership but not a full in-house security function. Learn more about our vCISO and advisory services.