
When it comes to protecting your business from most types of hacking, the best defence is a good offence. Having the right protocols in place to proactively protect your business is vital to keeping your systems safe. Since developing protocols for your business comes with research, education, & the proper understanding of hacking related to your organisation, we’ve provided a set of our most commonly asked questions to get you started.
Why am I being targeted by hackers?
Most likely you are being targeted because your system has a vulnerability that can be exploited. Hackers love easy targets, so they frequently seek out small businesses that might not have the type of protocols in place that we mentioned above. Most cyber-attacks are financially motivated, so if you are being targeted, it’s because someone suspects that you have something they want (data, included).
How many businesses are hacked each year?
Hacking statistics are a tricky thing. Some businesses don’t report when they fall victim to a cyber attack. Others will report some types of hacking and not others.
From what we do know, hacking is very common. In Australia, ASD’s ACSC received over 84,700 cybercrime reports through ReportCyber in 2024–25 – on average one every six minutes – and its Annual Cyber Threat Report 2024–25 notes that the vast majority of cybercrime still goes unreported. Overseas, a June 2015 Duke University survey reported that in the US, “more than 80 percent of U.S. companies indicate their systems have been successfully hacked in an attempt to steal, change or make public important data.”
How do companies get hacked?
Most of the time hackers get into a system due to human error. Many hacking techniques are designed to exploit a lack of understanding of how to prevent a security breach.
Business Insider explains, “While some exploits are caused by insanely technical code created to dupe even the most advanced machines, more often it's simple human actions that are to blame. Even the best protection software won't help someone with unsafe online practices.”
A few examples of these types of hacks include:
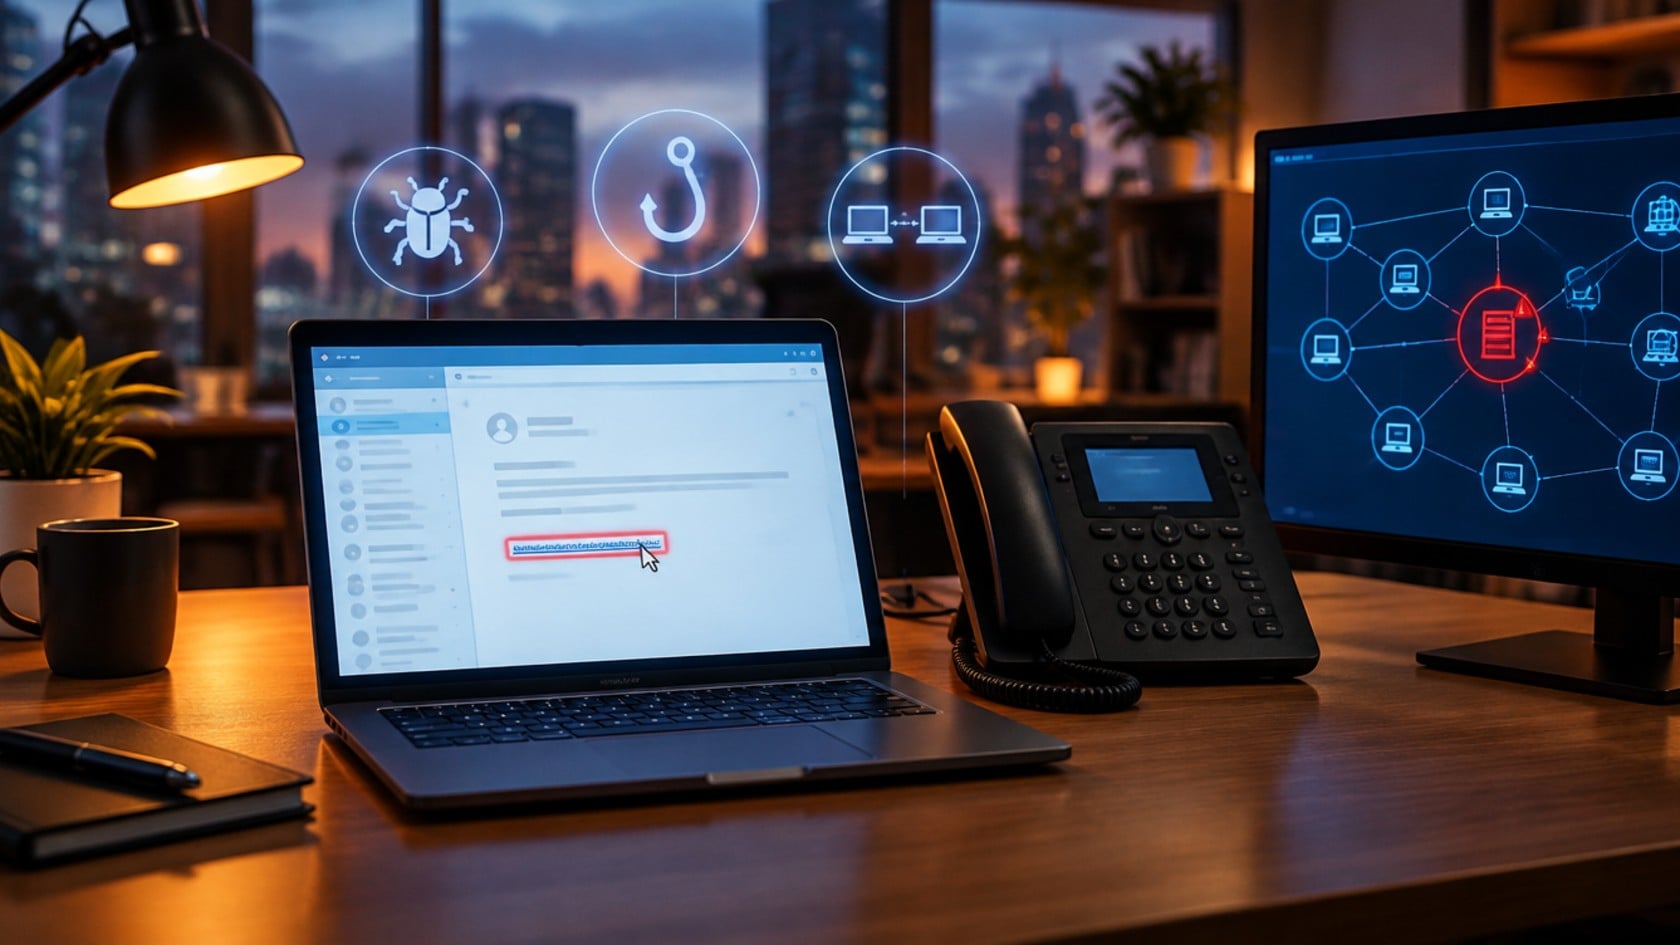
Malware
Malware is the installation of intrusive software on your computer. This most commonly happens through a dangerous web or email download, and due to a lack of prevention.
Phishing
Phishing attacks centre on tricking a user into revealing information in response to an email or other message. A particularly pervasive version of this is called “spear-phishing” which involves targeting an individual directly and fooling them into revealing usernames and passwords or other information. (Read more here: What is Phishing)
Man in the Middle
Man in the Middle (MitM) attacks are a common hacking technique where a hacker places themselves in between a user and an application. Sometimes this is an eavesdropping hack, and other times it involves intercepting or altering the data passed between them, such as login credentials, to gain access to computer systems.
Denial of Service
Denial of service (DoS) attacks flood a computer system, website or network with traffic or requests so that its rightful users can’t access it. Some attackers use them, or threaten to, as a way to extort a ransom. (Read more here: Denial of Service Attacks)
VoIP Hacking
We are frequently asked “can your business phone be hacked?” The simple answer is yes, it certainly can. This is especially true if you use a VoIP system as many companies do. In 2020, ZDNet reported that “hackers are exploiting unpatched VoIP flaws to compromise business accounts.”
Without the proper training and protocols in place, your business is at risk. Let our team of cybersecurity experts help you stay ahead of threats & attacks against your organisation.
If you’re worried about your business being hacked, contact StickmanCyber today to learn more about our cybersecurity and compliance services and our Security Operations services.
Frequently asked questions
How can you tell if your business has been hacked?
ASD lists warning signs such as emails or messages you didn’t send, logins or locations you don’t recognise, accounts logging you out unexpectedly, and files, settings or account details changed without your permission. Unfamiliar programs, or devices that become unusually slow, overheat or show unexpected errors, can also point to a compromise.
What should a business do if it has been hacked?
Act quickly: disconnect affected devices from the internet, change passwords, scan for malware and record what happened, as ASD’s recovery guidance advises. In Australia, report the incident through ReportCyber or call the Australian Cyber Security Hotline on 1300 CYBER1 (1300 292 371), available 24/7. If personal information is involved, the Notifiable Data Breaches scheme may also require you to notify the OAIC and affected people.
Are small businesses really targets for hackers?
Yes. Attackers often look for the easiest way in, and small businesses may have fewer security controls. ASD’s Annual Cyber Threat Report 2024–25 found the average self-reported cost of cybercrime for a small business was $56,600, up 14% on the previous year. ASD advises starting with the basics: multi-factor authentication, strong and unique passphrases, regular software updates and staying alert to phishing.
Should a business pay a ransom after a ransomware attack?
ASD advises never paying a ransom: there is no guarantee you will regain access to your information or stop it being sold or leaked, and you may be targeted again. Under the Cyber Security Act 2024, businesses with an annual turnover of $3 million or more that make a ransomware or cyber extortion payment must report it to ASD within 72 hours.
What is ethical hacking?
Ethical hacking is authorised testing in which security specialists use the same techniques as attackers to find weaknesses before criminals do. The most common form for businesses is penetration testing, which simulates real attacks on networks, applications or people within an agreed scope. It is done with the owner’s permission, and the findings are reported so the weaknesses can be fixed.