
Incident response is the set of processes and policies an organisation follows when a cyber incident, such as an attack or a data breach, occurs. Its aim is to limit the damage: shortening recovery and cutting the effort, cost and reputational harm that follow an attack or breach. A well-run response also helps an organisation learn from each incident and reduce the risk of future attacks on its information security.
In this post, we look at a basic incident response template.
Below are five key steps of Incident Response template that every organisation should consider:
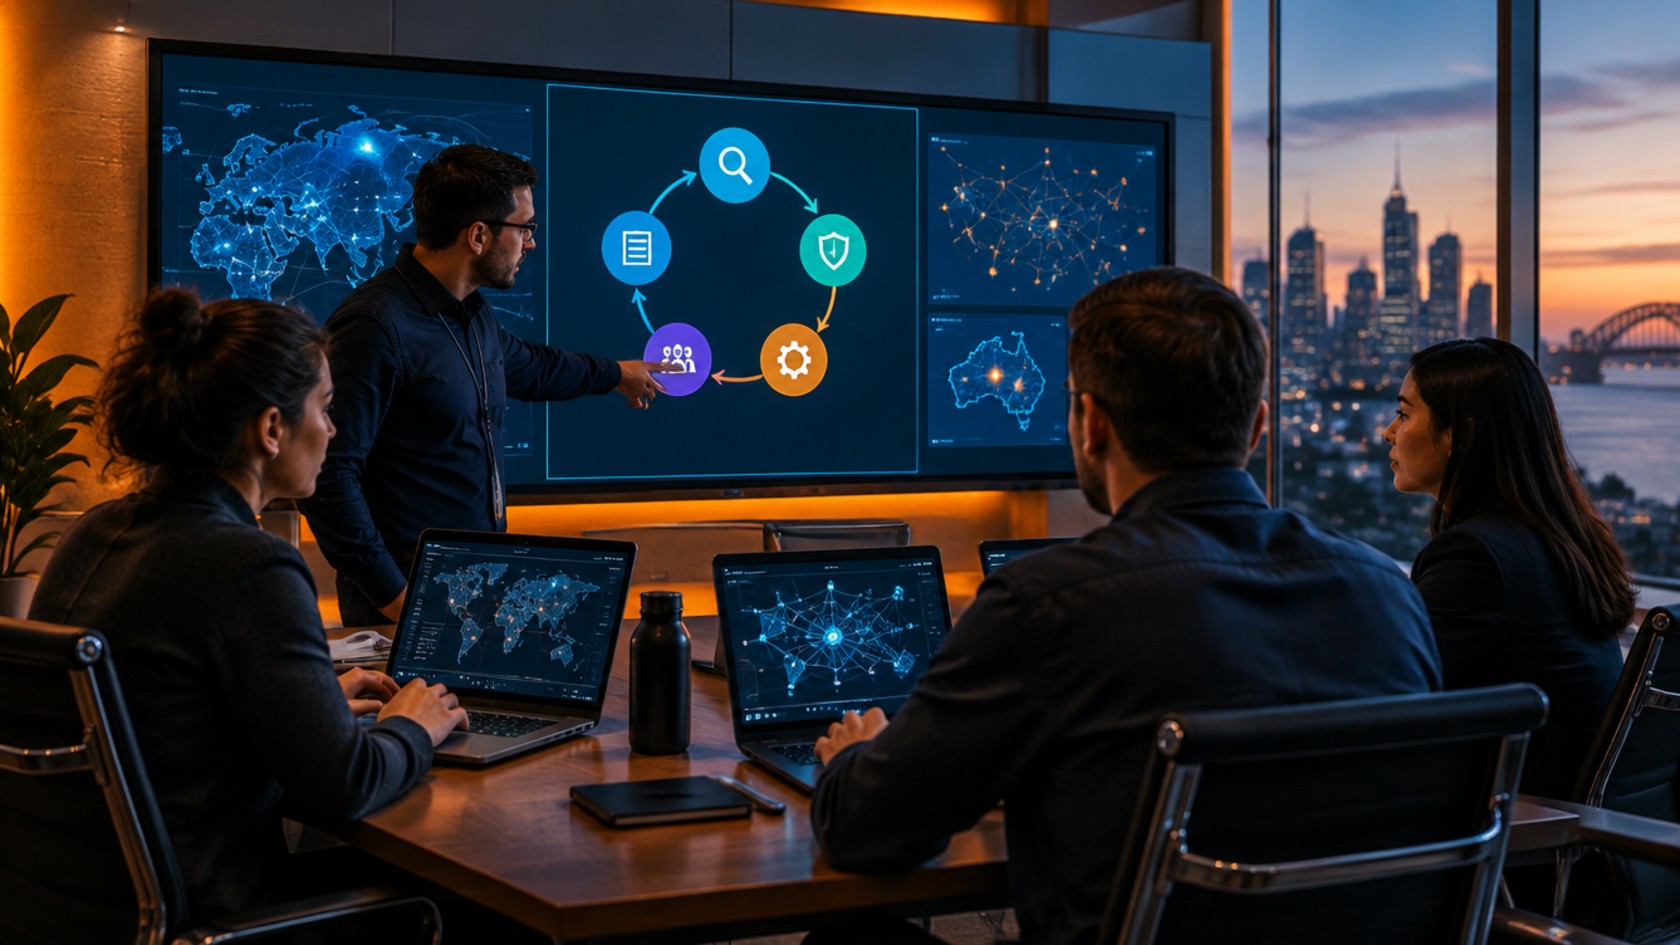
Incident Response management is customisable and unique to each organisation but usually consists of five key steps that exist as a life cycle that occurs every time a cyber incident takes place. Below are these five steps explained:
Preparation & Planning
During this stage of the life cycle, organisations evaluate the effectiveness of their existing security measures and policies in place. Evaluation usually consists of identifying vulnerabilities via assessments or scans which helps in prioritising which type of incidents need to be responded to as soon as they are identified. The main function of this phase is to improve existing policies and procedures even if they have to be re-written.
Identification
In this second phase of the life cycle, Incident Response teams work on identifying the presence of any suspicious activity within their organisation, by utilising the procedures outlined in the preparation and planning stage. In the event that a threat is identified, a detailed analysis of its origin, its type as well as the goals of the attackers needs to take place. During this phase, it is critical that Incident Response teams collect and document all the evidence found. Once this information has been procured, it needs to be effectively communicated across the organisation. Using plans established in the prior phase, stakeholders, authorities and legal counsel need to be alerted and instructed on the steps that need to be taken now that a cyber incident has occurred. In Australia, this can include reporting the incident to ASD’s ACSC and, for organisations covered by the Privacy Act, notifying the OAIC and affected individuals of an eligible data breach under the Notifiable Data Breaches scheme.
Containment & Elimination
After the identification of a threat the next step is to contain and eliminate it. Organisations should prioritise getting to the containment stage as quickly as possible so that repercussions of the attack can be controlled and mitigated. There are two key ways containment can be achieved, short-term and long-term.
Short-term containment refers to the process of isolating immediate threats, for example, this may involve segmenting networks or turning servers offline that have been affected by the attacker. Long-term containment on the other hand involves more durable measures, such as tightening access controls on unaffected areas, to lower the chance of the attack spreading across infrastructure.
Once the threat has been contained and an understanding of its extent has been achieved, organisations need to work on elimination. Security teams can begin ejecting attackers and eliminating malware from systems. This phase continues until all traces of the attack are removed.
Recovery
In this fourth stage of the life cycle, organisations bring patched and updated replacement systems online. In a perfect scenario systems can be brought online without any data loss, but more often than not, teams must determine when the last clean copy of data was created and restore from it. The recovery phase also involves security teams monitoring networks and systems for a period after the attack to make sure malicious actors don’t return.
Feedback & Improvement
In the final stage of the life cycle, organisations review how effective their incident response was and what can be done better next time. This stage also involves security teams completing thorough documentation of events for later review or reference.
So that is a basic 5-step incident response template that you can use as a base to build your incident response plan, customised to your unique business needs.
Does your organisation already have an incident response plan? StickmanCyber’s experts can review your current cyber security setup and help you set up the right incident response plan for your business.
Frequently asked questions
Is there a free incident response plan template for Australian organisations?
Yes. ASD’s Cyber security incident response planning: Practitioner guidance acts as a cyber security incident response plan (CIRP) template, and ASD also provides a separate fill-in template. Its appendices include a readiness checklist and templates for situation reports, incident logs and evidence registers. ASD notes each plan should be tailored to the organisation’s own environment, priorities, resources and obligations.
What is the difference between a cyber security event and a cyber security incident?
ASD defines a cyber security event as a system, service or network state indicating a possible breach of security policy, failure of safeguards or a previously unknown situation relevant to security, such as a user disabling antivirus. An incident is an unwanted or unexpected event, or series of events, that has compromised business operations or has a significant probability of doing so.
How should evidence be preserved during a cyber incident?
Your plan should set out who collects, preserves, handles and stores evidence, and within what timeframes. ASD recommends keeping a detailed log of who collected or handled each item, the date and time (including time zone) and identifying details such as hostnames and IP addresses. Common evidence includes host images, network packet captures, log files, configuration files and screenshots. Seek advice from digital forensic professionals, legal advisers or law enforcement if needed.
What is a situation report in incident response?
A situation report is a regular update that keeps decision-makers informed while an incident is being managed. ASD suggests it can include the incident’s date and time, status, type and classification, scope and impact, severity, any external assistance required, actions taken so far, contact details for key response team members and the date and time of the next update.
What is the difference between a hot debrief and a formal debrief?
A hot debrief is held immediately after systems, services or networks have been recovered, so the response team can share feedback while details are fresh and urgent issues can be fixed straight away. A formal (or cold) debrief is held days to weeks later. ASD suggests the formal review explore root causes, whether the incident could have been prevented and how the response could be improved.
What should an incident response readiness checklist cover?
ASD’s readiness checklist starts with preparation: a cyber security policy or strategy that sets your position on matters such as paying ransoms and reporting incidents to government, and an incident response plan that aligns with your emergency management and business continuity processes and has been reviewed or tested in an exercise. It also checks that response staff are trained and that up-to-date hard copies of the plan and playbooks are stored securely.